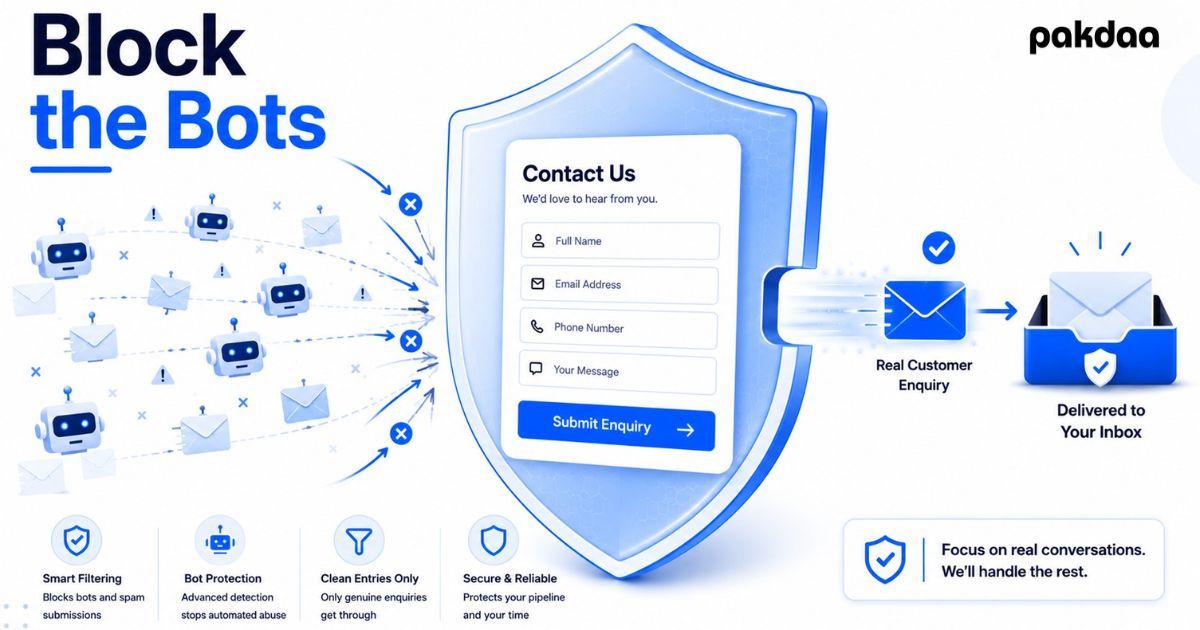
Open your inbox and there they are: ten fake enquiries about SEO services, crypto, and links you did not ask for. Annoying, yes. But here is the part most owners miss: form spam does not just waste your time. It buries the real leads sitting right next to it.
When junk floods your form, genuine enquiries get lost in the noise, deleted by accident, or blocked entirely when you tighten filters too hard in frustration. So the goal is not just to protect your contact form from spam. It is to block bots without blocking the customers you paid to reach.
That balance is the whole game. Here is why spam happens, every method that stops it, and how to set up protection that stays invisible to real people.
Why your contact form attracts spam
It is rarely personal. Bots crawl the web looking for any form they can submit, then fire junk at it automatically, thousands of forms at a time. Automated bots make up a huge share of all web traffic, with reports commonly putting bad and good bots together at close to half of it.
Your form is a target simply because it exists and it is easy to submit. Anything a human can fill in, a script can fill in faster, unless you give it a reason to fail.
The real cost of form spam
The obvious cost is wasted time sorting junk. The hidden cost is worse.
When spam volume is high, real enquiries get missed in the pile or deleted along with the junk. Then owners overreact and add aggressive filtering that also blocks genuine customers. Both outcomes cost you leads. Spam is actually one of the sneaky ways a form loses real enquiries, which we cover in our guide to why your contact form loses leads.
Spam protection methods, ranked
Not all defences are equal. The best ones stop bots while staying completely invisible to humans. The worst add friction that costs you real leads. Here they are, weakest human-experience first is a myth, so this ranks by the balance of protection and low friction.
Notice the pattern: the quiet methods at the top add zero friction. Start there. Save the visible challenges for when you actually need them.
The quiet methods, explained
These do most of the work and no real customer ever notices them.
Honeypot
A honeypot is a hidden field that humans never see, because it is tucked away with styling. A bot fills in every field it finds, including that one. So if the hidden field has content, you know it was a bot and you reject it. Simple, invisible, and surprisingly effective.
Time trap
Bots submit forms in milliseconds. A real person takes a few seconds to type. Record the time between page load and submit, and reject anything suspiciously fast. Humans never trip it.
Server-side validation
Never trust checks that run only in the browser, because bots skip the browser entirely. Re-check every submission on the server: valid email, required fields, sensible length. This alone stops a lot of low-effort junk.
Rate limiting
If one source fires twenty submissions in a minute, that is not a customer. Limit how many submissions can come from the same place in a short window and you shut down bulk spam runs.
When CAPTCHA is worth it
CAPTCHA works, but it is not free. Every visible challenge you add costs you a few real people who cannot be bothered or get it wrong. So treat it as a last layer, not a first.
Invisible reCAPTCHA, which scores behaviour quietly in the background, is a good middle ground. Reserve the image-puzzle kind for forms under heavy, persistent attack, where the spam cost outweighs the friction. For most businesses, the quiet methods above plus invisible scoring are enough.
The golden rule: block bots, not humans
Every layer of protection you add is a small tax on real customers. So layer invisible defences first, measure, and only escalate to visible challenges if spam is still getting through. A form that stops every bot but also loses 10% of real enquiries is not a win.
How to set up spam protection that works
Here is the order to build it, quietest first.
Step 1: Add a honeypot field
Start with the honeypot. It is invisible, cheap, and catches a large share of basic bots immediately.
Step 2: Add server-side validation and a time check
Validate every submission on the server and reject anything submitted unrealistically fast. This stops most automated junk without touching the user experience.
Step 3: Add rate limiting
Cap submissions from a single source in a short window to kill bulk spam runs.
Step 4: Add invisible scoring, then CAPTCHA only if needed
If spam still leaks through, add invisible behaviour scoring. Only add a visible CAPTCHA as a final resort on forms under heavy attack.
Step 5: Store every submission so nothing is wrongly lost
Save all submissions, even flagged ones, so a false positive never quietly deletes a real lead. This is another reason to store submissions rather than rely on email, which we cover in our guide to storing form submissions instead of emailing them.
Step 6: Monitor and adjust
Check what is getting through and what is being blocked. Spam evolves, so tune your layers over time rather than setting and forgetting.
The bottom line
Form spam is a lead problem in disguise. Left alone it buries real enquiries, and over-corrected it blocks real customers. The fix is to protect your contact form from spam with quiet, invisible defences first, honeypots, time checks, validation, and rate limiting, and reach for CAPTCHA only when you truly must. Block the bots, keep the humans, and store everything so nothing real slips away. If you want this set up cleanly, that is what our team does.
Buried in form spam?
We will add quiet, invisible spam protection to your contact form that blocks bots without adding friction for real customers, and make sure no genuine lead is ever lost. Free to scope.
Book a free form audit